
Spotify Gets Hit Again
Last updated:
Protection against credential stuffing isn’t something that a company like Spotify should struggle with, and suffering two credential stuffing incidents in one quarter shows a sloppy attitude toward security.
As many as 100,000 of the music streaming service’s customers could face account takeover.
Spotify has returned for another appearance with a credential stuffing disaster eerily similar. This time, data for approximately 100k users appeared in an Elasticsearch instance spotted by researchers. This is distinctly different data than the load that researchers discovered in November 2020.
No specifics were listed about the stolen data, but Spotify users should reset their account passwords and be on the lookout for spear phishing attempts.
“Spotify streaming music aficionados are in the crosshairs of yet another credential-stuffing cyberattack, just three months after the last one. The service has forced password resets for impacted users.
Cybercriminals carrying out credential-stuffing take advantage of people who reuse the same passwords across multiple online accounts. Attackers simply build automated scripts that systematically try stolen IDs and passwords (either gleaned from a breach of another company or website, or purchased online) against various types of accounts.”
Related reading: managed IT in Vancouver, WA, Why Passwords are Your Business’s Weakest Point.
Request an IT assessment
Tell us a little about your business and a PDX IT team member will follow up to schedule an assessment. Prefer to talk? Call 971-331-4871.

About the author: Steve Shaff
Steve Shaff is the owner of PDX Information Technology Services, a managed IT provider he founded in 2020. From the Tualatin office he helps businesses across Portland Metro & Southwest Washington with IT support, cybersecurity and compliance. More about Steve · Contact PDX IT
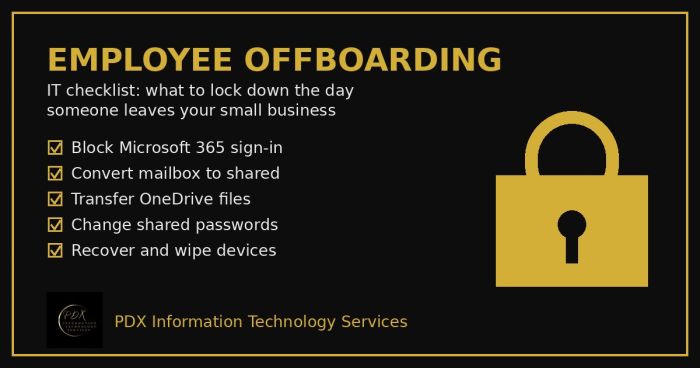
Portland employee offboarding IT checklist: lock Microsoft 365, save the mailbox and OneDrive files, change shared passwords and wipe company devices.
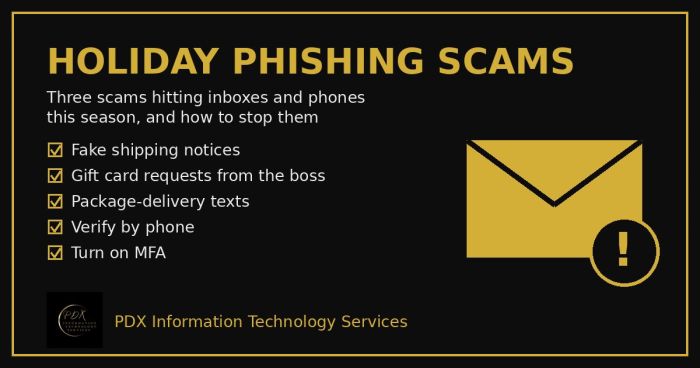
Holiday phishing scams are hitting Portland small businesses: fake shipping notices, gift card requests from the boss and delivery texts. How to stop them.
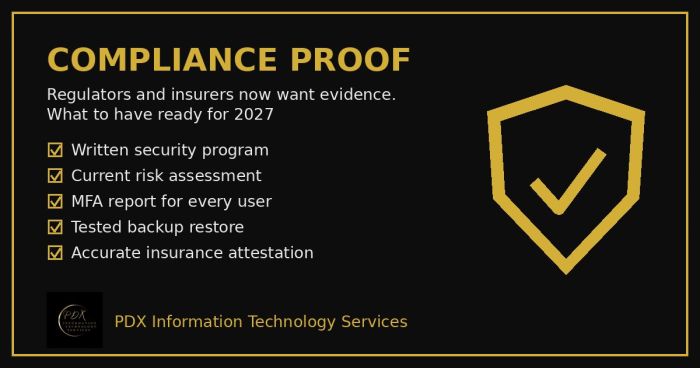
Cybersecurity compliance proof: HIPAA, CMMC, the FTC and cyber insurers now want documented evidence, not promises. See the checklist for 2027.